Project · One-time secret links
VaultShare
Share a password or key through a link that works once, then destroys itself.
Encrypted with AES-GCM and shredded after the first read.
- Type
- Personal open-source project
- Automated tests
- 22 (pytest)
- Built with
- Python · FastAPI · cryptography (AES-GCM)
- Live demo
- Runs locally — not hosted
Overview
What it does
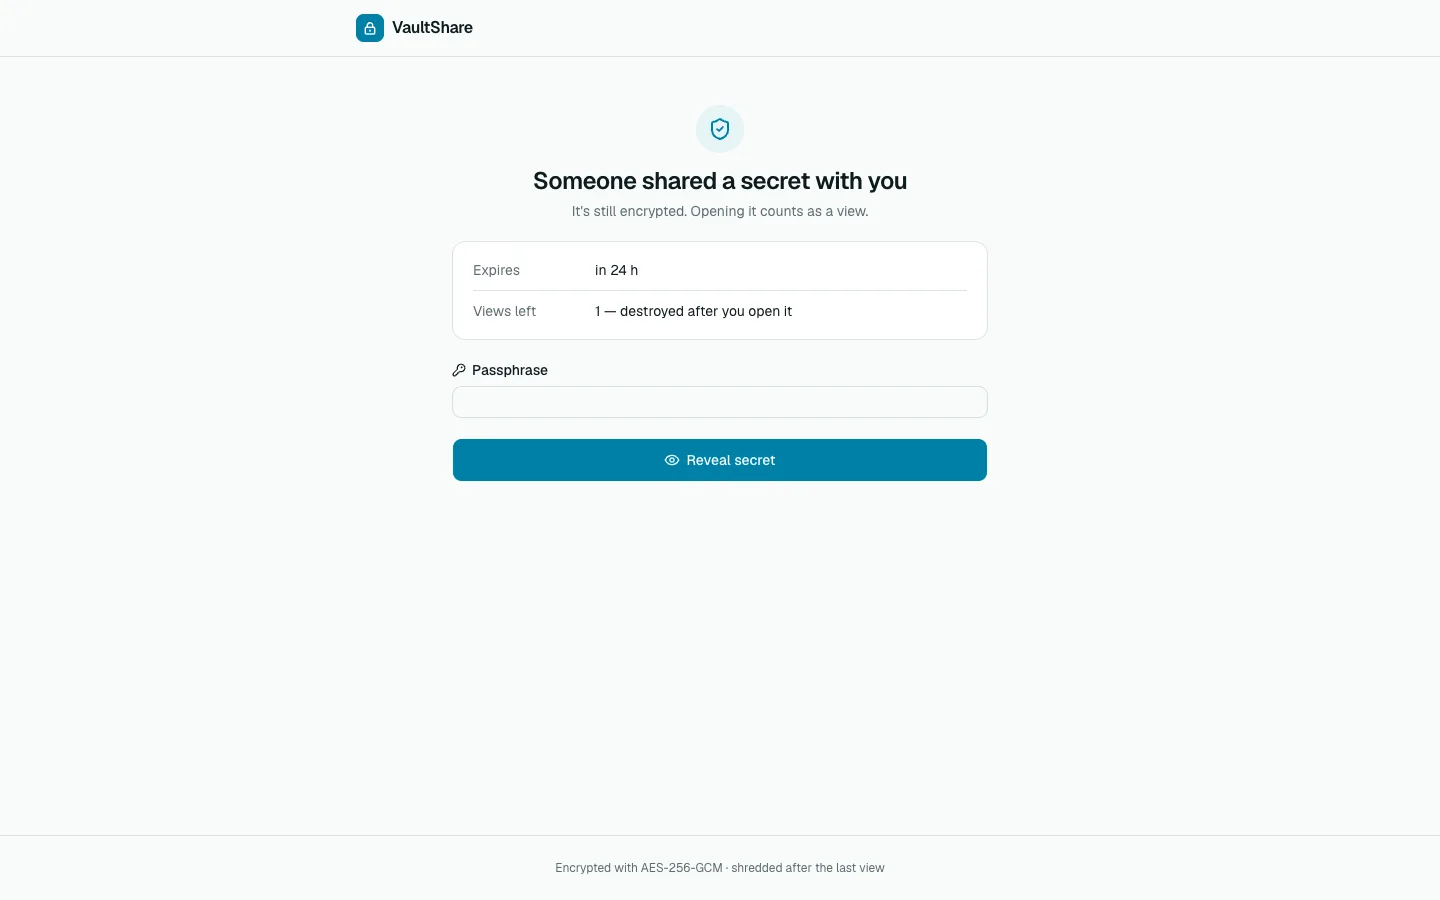
VaultShare turns a password, API key or small file into an encrypted link that expires and destroys itself after it's read. A passphrase can be sent over a second channel, and recipients see nothing until they press Reveal — so chat-app link previews can't burn the secret.
Screenshots
From the running application
Reveal page that shows nothing until the recipient presses Reveal 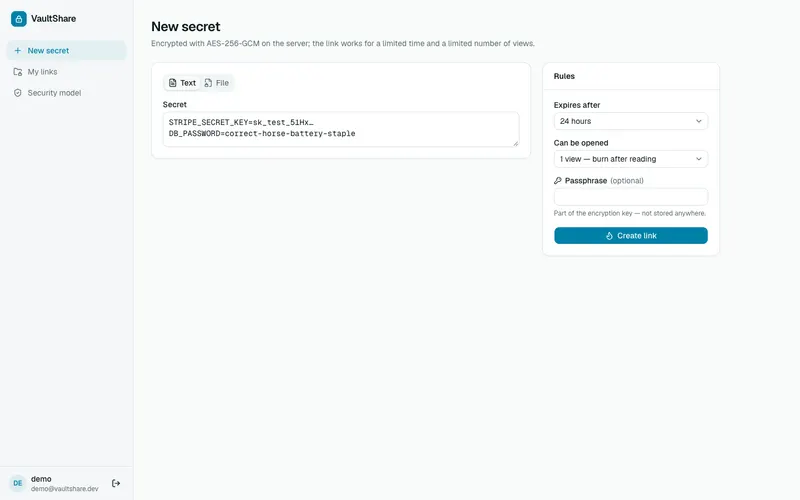
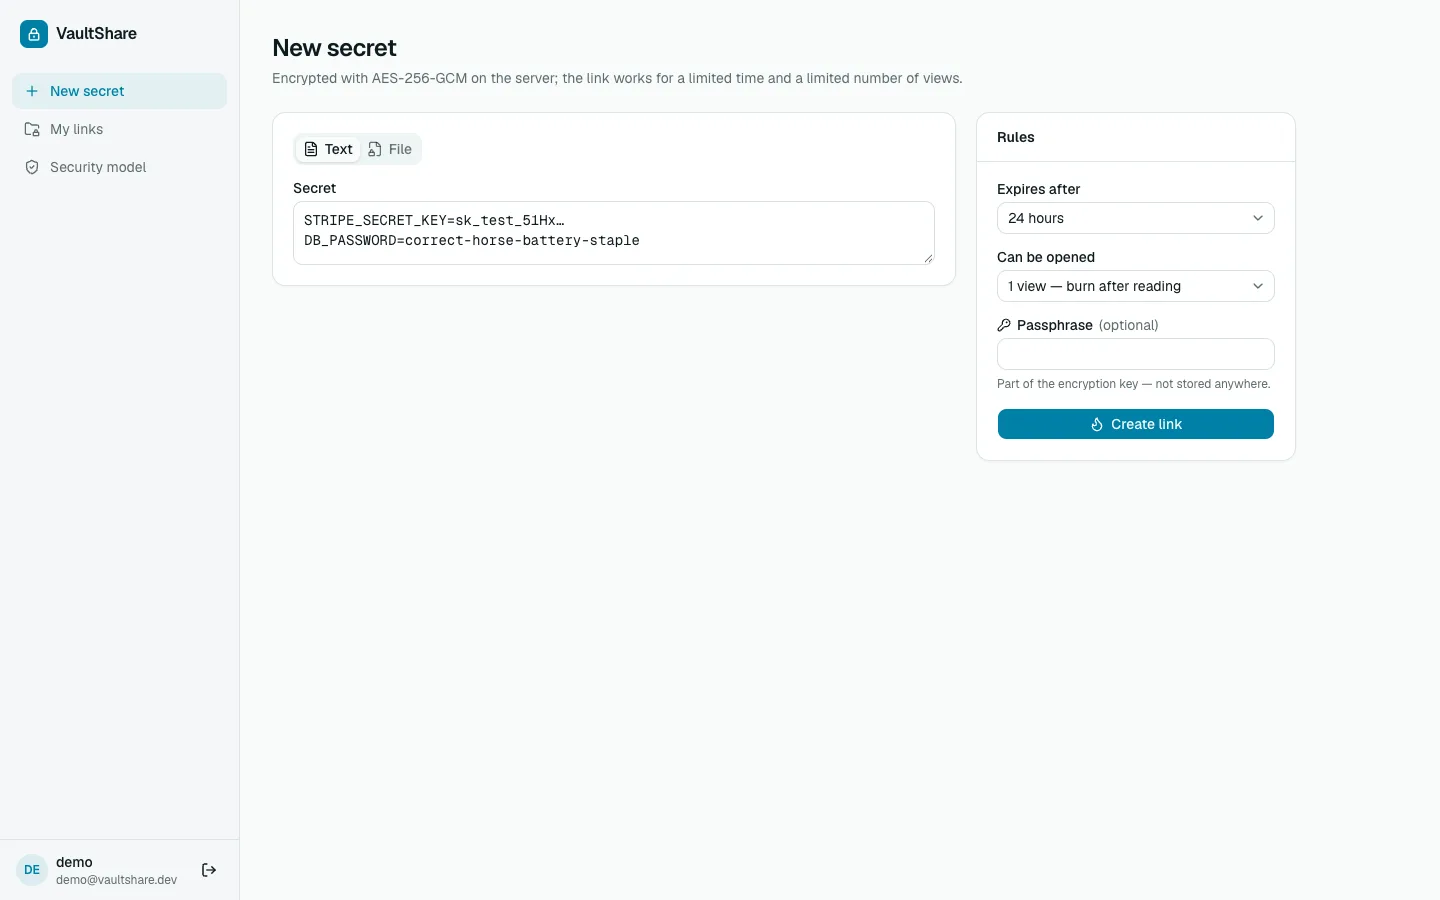
Create a secret link with expiry and passphrase 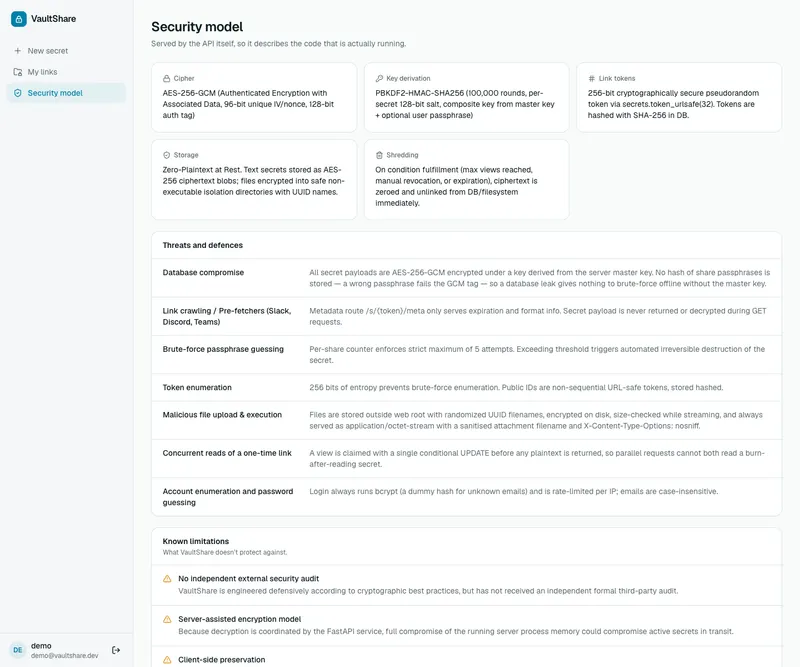
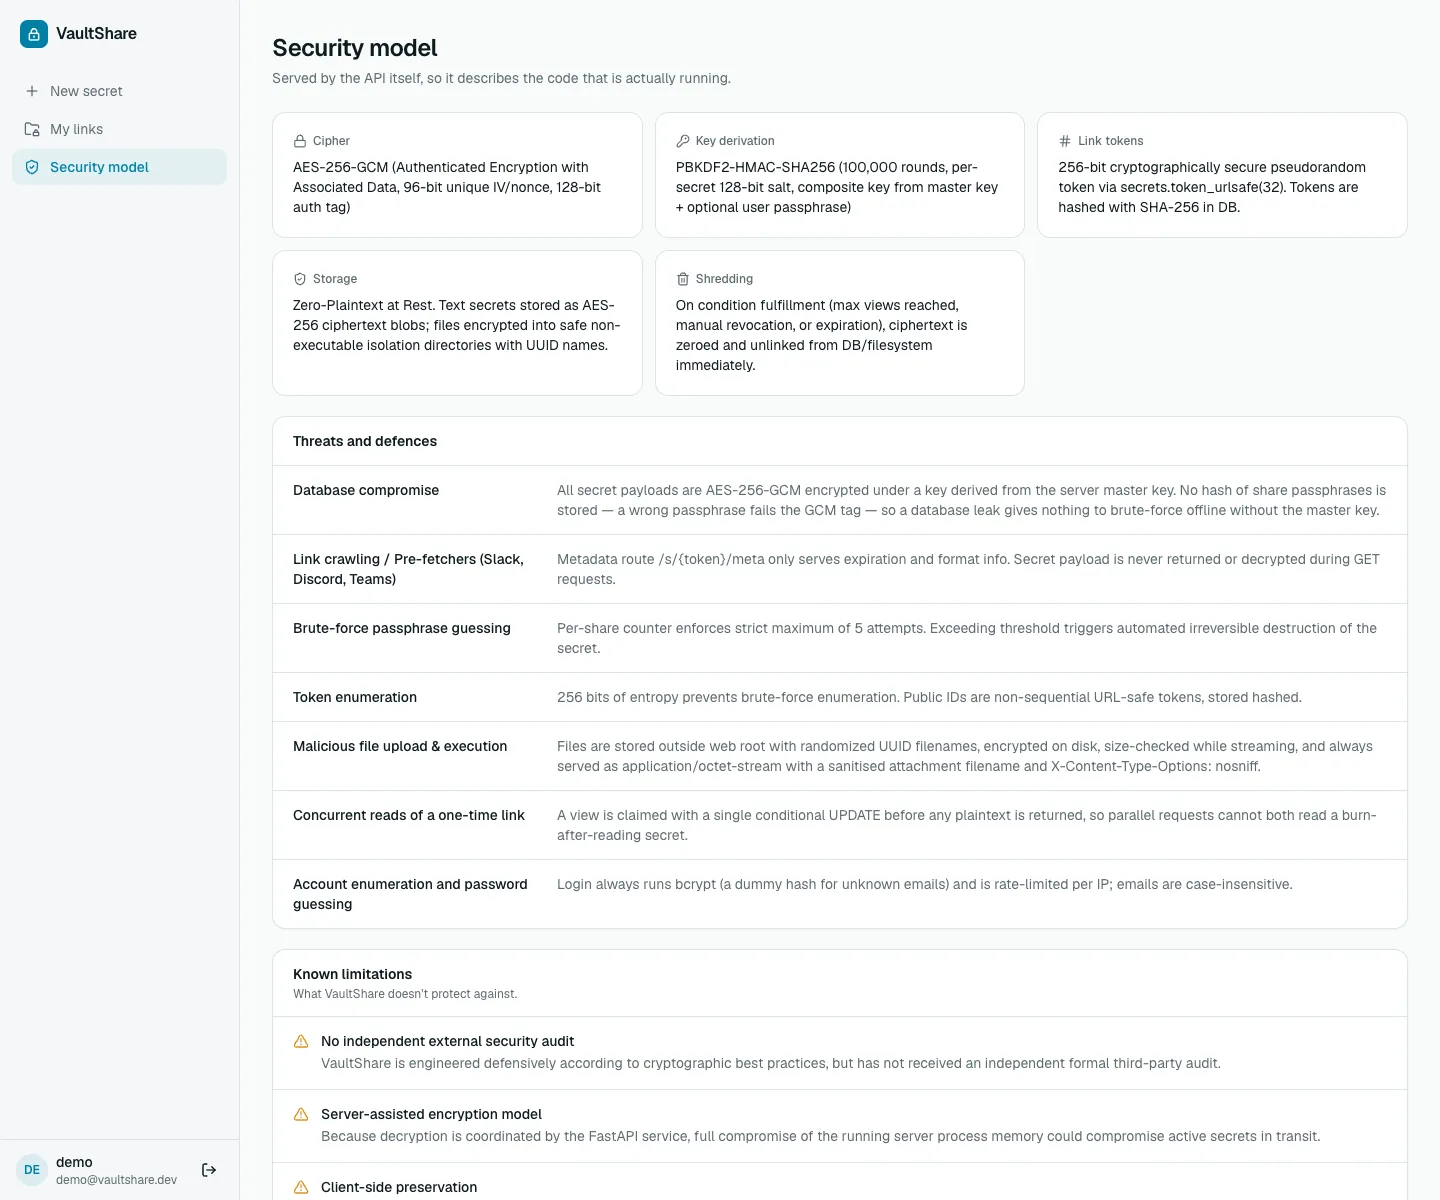
Published threat model
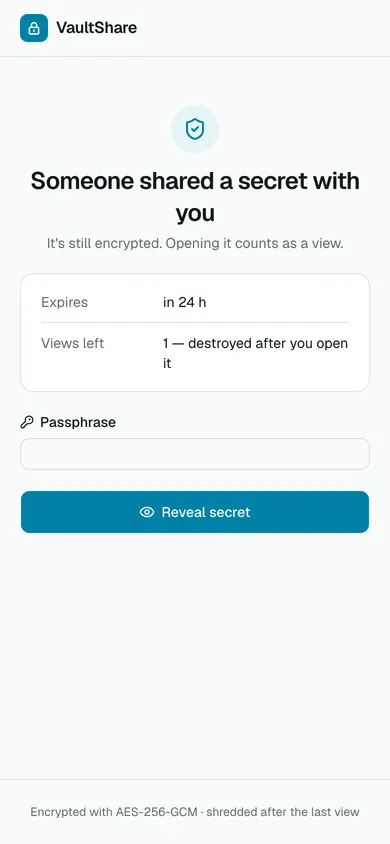
Reveal on a phone
Captured from the app running locally with its seeded demo data. Select an image to open it full size.
Core features
What's in it
AES-256-GCM
Secrets encrypted at rest with a master key; nothing stays readable, even for the sender.
Atomic view claims
Two simultaneous opens can't both read a one-time secret.
Reveal button
Link previews from chat apps don't consume the secret.
Threat model
What it protects against — and what it doesn't — is documented.
Stack & skills
Built with
Technology
- Python
- FastAPI
- cryptography (AES-GCM)
- SQLAlchemy (async)
- Next.js
- TypeScript
What this project demonstrates
- Applied cryptography
- Concurrency safety
- Security writing
Repository & demo
Run it yourself
Seeded demo account: demo@vaultshare.dev (password in the README).
No public live demo is hosted. Everything below runs locally with Python 3.12+ and Node 20+.
$ git clone https://github.com/Moeijiro/vaultshare.git
$ cd vaultshare
$ make install
$ make seed
$ make api
$ make web
Have a project in mind?
I build APIs, automation systems, Discord integrations and full-stack applications. Tell me what it should do and I'll tell you how I'd build it.